AurionMail Suite delivers a seamless Proton-like experience on a 100% open-source stack, orchestrating CryptPad and JMAP email into a unified workflow.
Bridge the gap between closed commercial clouds and fragmented self-hosted alternatives.
| Feature | Proton Suite | Nextcloud + Mail | Standard CryptPad | AurionMail Suite |
|---|---|---|---|---|
| 100% Open Source & Self-Hosted | Proprietary Backend | Yes | Yes | Yes |
| E2EE Email & Documents | Yes | Complex / Plugins | N/A for email | Yes |
| Unified Single Password | Yes | Fragmented / Manual PGP | Fragmented | Yes |
| Open Standards (OpenPGP, JMAP) | Limited | Yes | N/A for email | Yes |
Designed from the ground up for strict privacy, ease of use, and self-hosted control.
Authenticate once per session. Your master password derives client-side keys to decrypt both your emails and CryptPad documents simultaneously.
Logging out from either Webmail or CryptPad instantly clears state and logs you out across all apps and active sessions globally.
Seamlessly sync PGP and document encryption keys across authorized user devices without compromising Zero-Knowledge architecture.
Sysadmins can provision LDAP accounts as they usually do. Users initialize their master password safely via /init.
CryptPad has been visually overhauled to deliver a sleek, modern, cohesive design theme across the entire suite.
Upcoming features include dynamic emergency URLs for instant account hold or complete self-destruction upon compromise.
Explore the clean, unified interface across email and document workspace.

Single Sign-On & Client-Side Key Derivation

Bulwark Webmail with Seamless OpenPGP

Refreshed Modern CryptPad Integration

OpenPGP Key Management & Password Sync
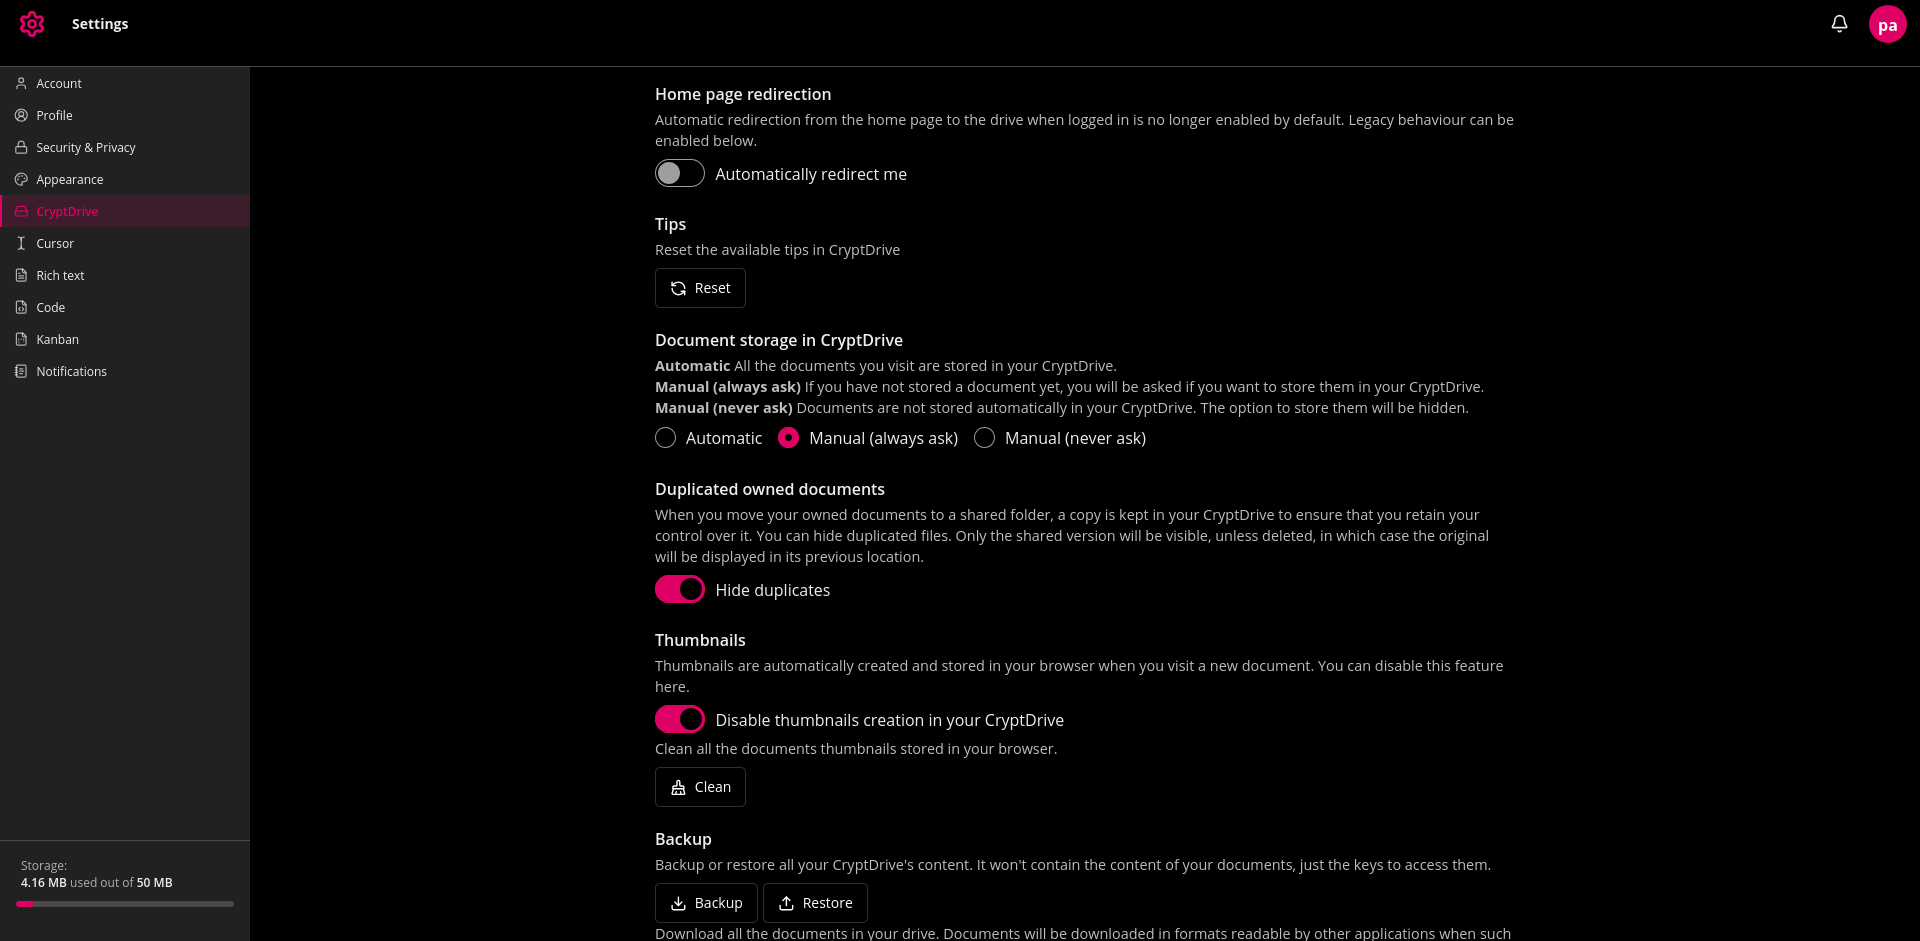
CryptPad & Email Preferences

Clean Session Teardown & Purge
Explore the sub-modules comprising the AurionMail ecosystem.
Frontend for authentication and Zero-Knowledge key derivation.
All-in-one binary covering Hydra, SSO, Bulwark, Bridges, & CryptPad.
Extension enabling end-to-end OpenPGP mail encryption in Bulwark.
Central orchestrator for key syncing, session state, and inter-app communication.
Lightweight bridge scripts for secure secret sharing during auth routines.
Customized CryptPad with embedded SSO integration and refined UI styling.
Secrets are kept strictly in client RAM using Argon2id and HKDF derivation. Cross-origin secret transfers use non-extractable AES-GCM keys with server-side ephemeral RAM storage (5-minute max TTL with Burn-on-Read guarantees).